No agents, no long deployment. Point TRaViS at your domains and it maps your surface the way an attacker would — then scores it, explains it, and tells you what to kill first. Here's how.
Several layers of discovery, from the attacker's point of view, surface the assets you own and the ones you forgot.
Hidden and forgotten hosts via certificate transparency, DNS, and proprietary enumeration — including dev/staging nobody inventoried.
Leaked keys, tokens, and reused logins across the open and dark web — the credentials that open admin portals.
Undocumented and deprecated endpoints plus domain-wide JavaScript analysis — the shadow surface security never got told about.
Shadow LLM endpoints, exposed model APIs, and MCP servers on your perimeter — the AI attack surface nobody is watching.
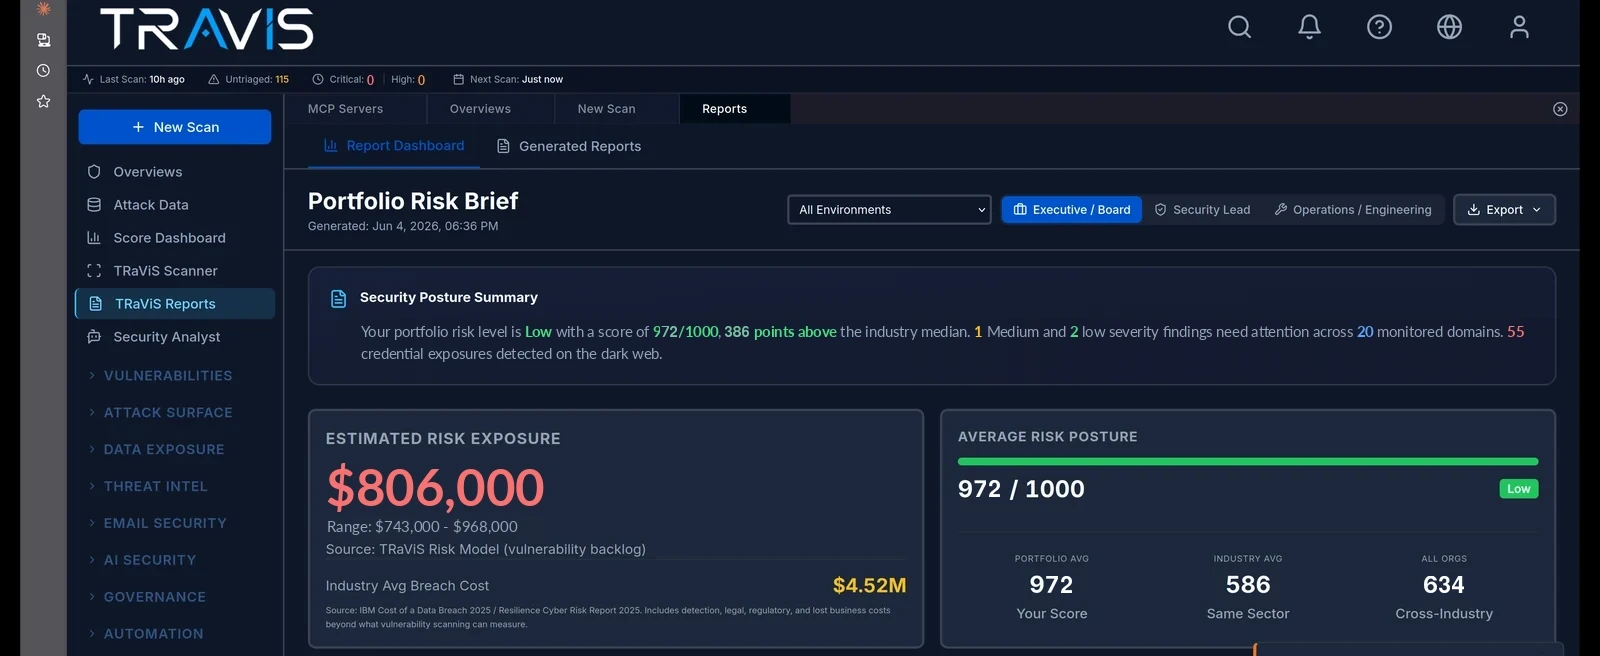
Every finding rolls up into a single 0–1000 posture score, benchmarked against your sector and translated into estimated dollar exposure — the board-ready answer, generated continuously.

Posture scored against your sector, breach risk quantified in dollars, exported for the board in a click.
Catch exposures as your surface changes — feed findings into the pipeline, not a quarterly review.
Push findings to your SIEM and existing workflow so nothing lives in yet another dashboard.
Executive, security-lead, and engineering views — exported as CSV, JSON, or a board-ready brief in a click.